A price-check script fetches product pages from a shop. Without a proxy each page comes back in under half a second; through the proxy every request takes two or three seconds, and a batch meant to finish over lunch runs into the afternoon. The proxy gets the blame, but the seconds could just as well come from a distant exit, a fresh connection for every request or a shop that answers more slowly on purpose.
Below, we split one proxied request into its stages, measure each with a single curl command (with real output from our test machine) and go through the usual causes in the order you can check them. A symptom table closes the article.
What does "slow" mean for a proxy?
"Slow" covers two problems: a long wait before anything arrives, and a download that crawls once started. The first is latency, the time a request spends travelling and waiting; the second is throughput, how much data per second flows. Most proxy complaints are about latency, because pages and API answers are small. Our guide to latency and how it differs from ping explains both terms.
Before you measure speed, make sure the proxy is really in use and exits where you chose. A proxy that silently falls back to a direct connection produces timings that mean nothing; how to test a proxy covers the IP, location and leak checks.
Where does the time go in a proxied request?
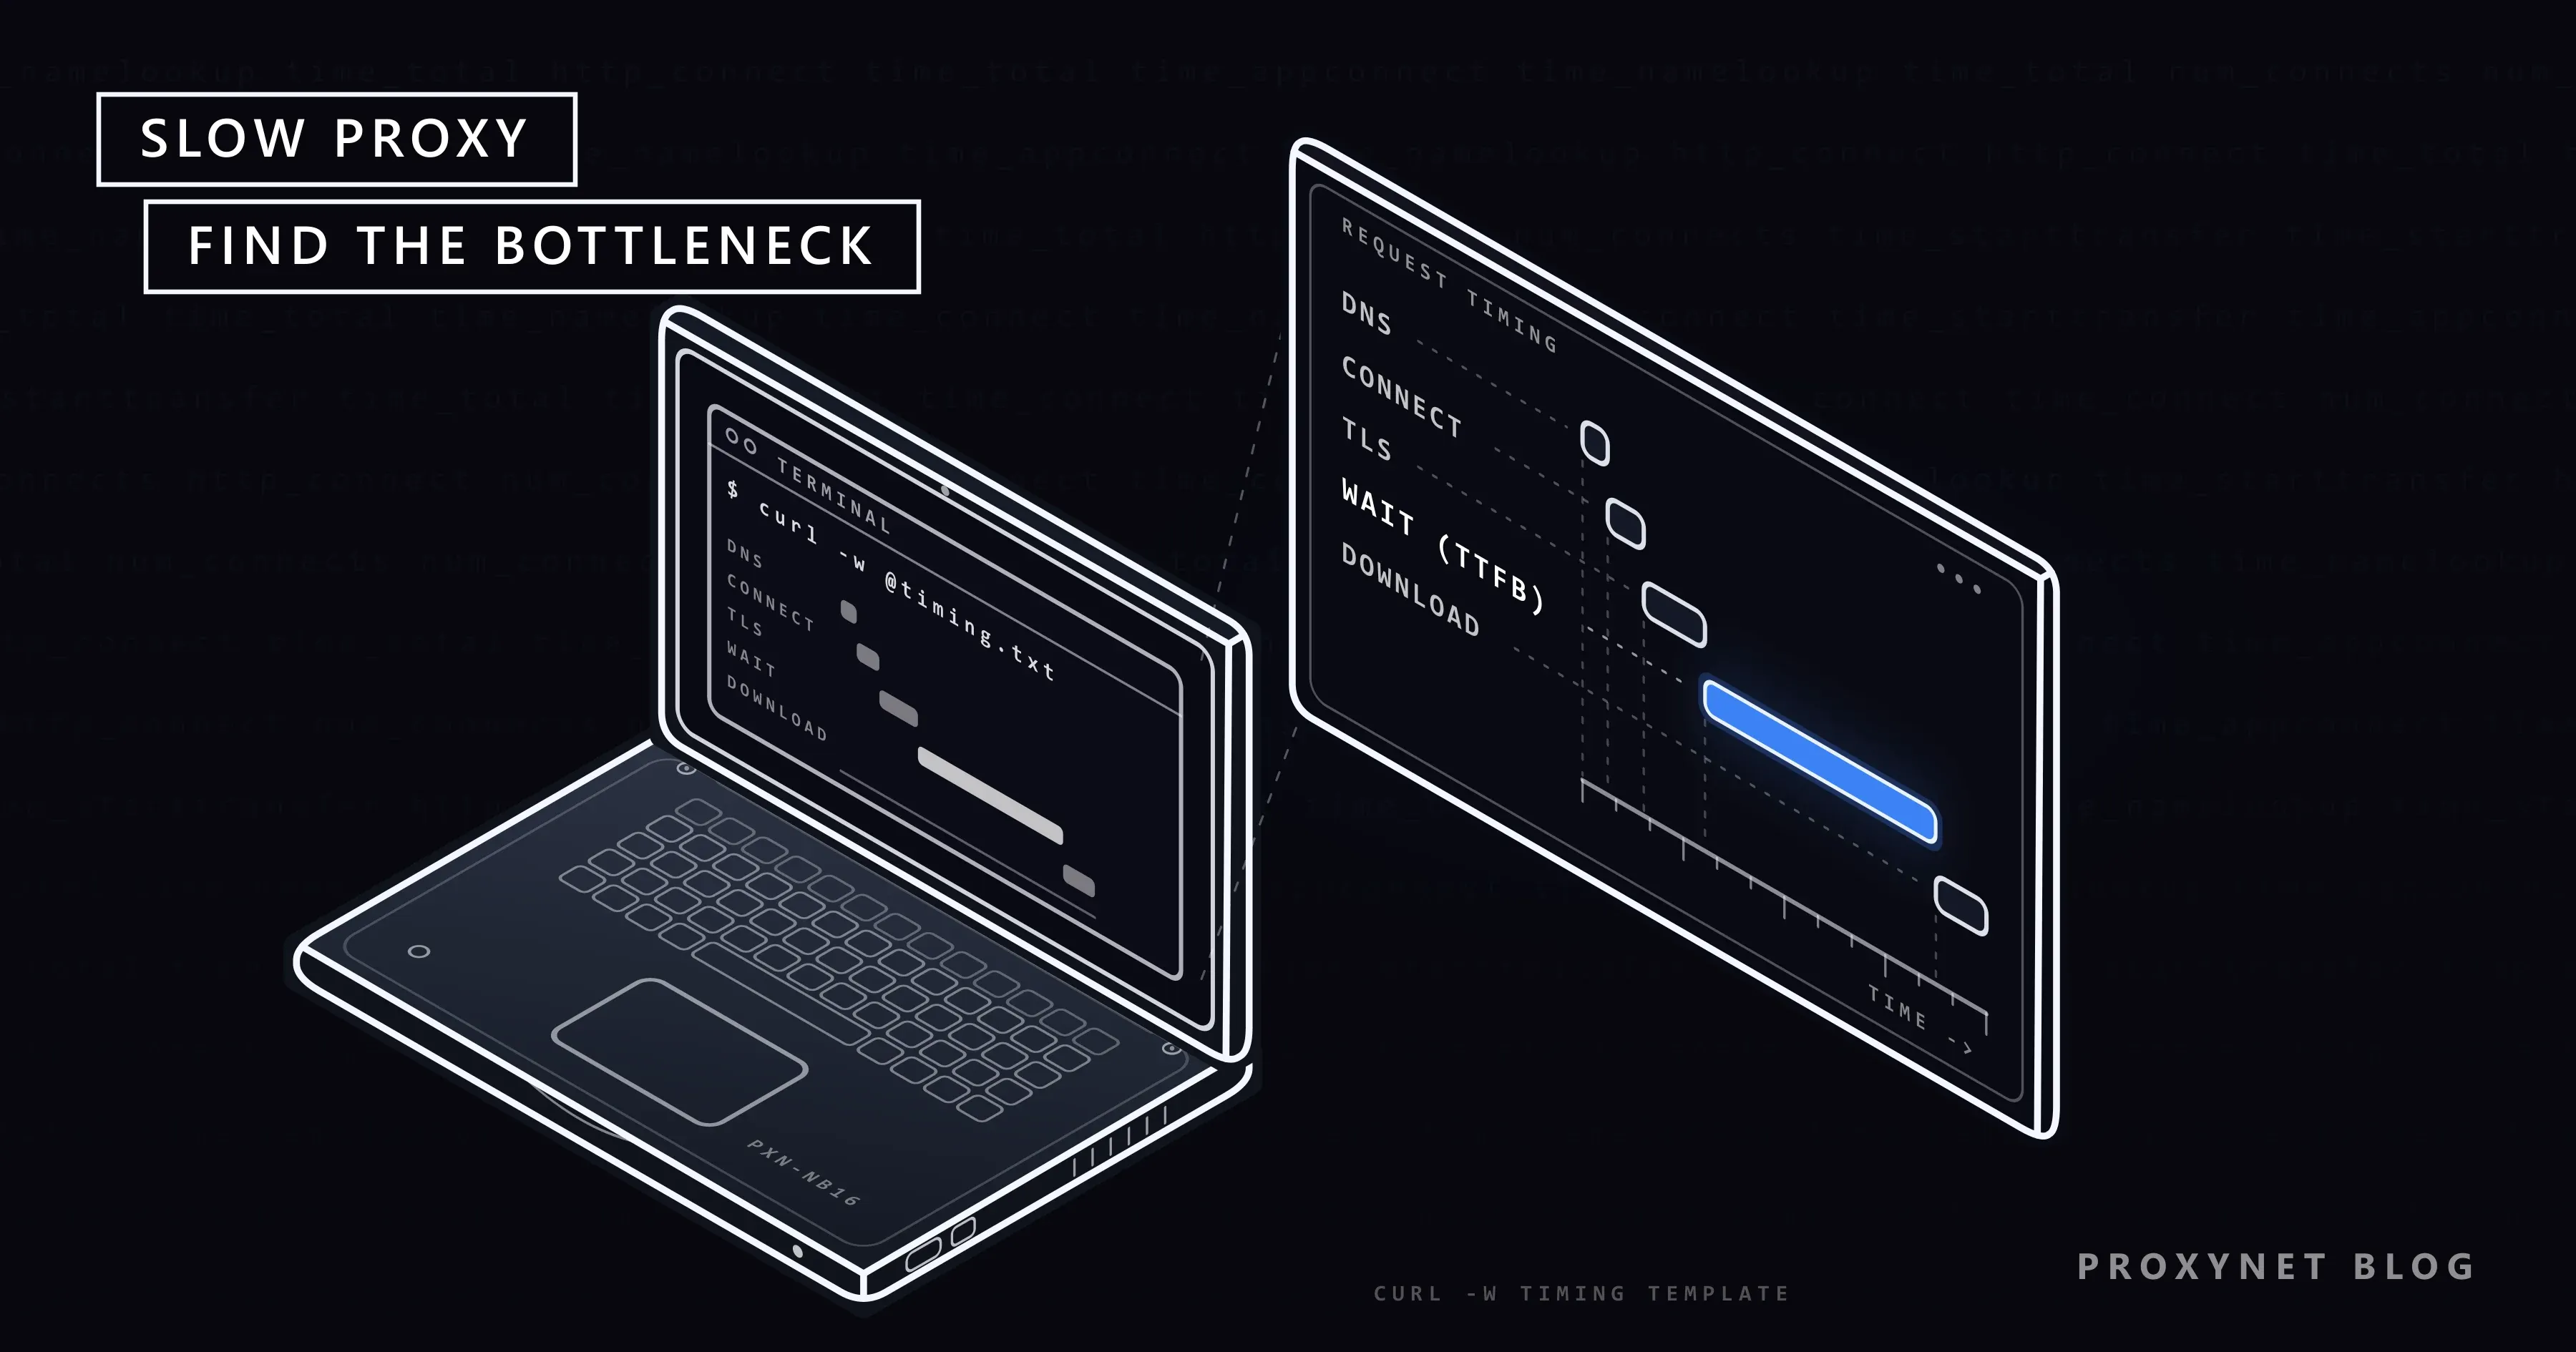
A request through a proxy passes through six stages, and each one can be the slow part. For an HTTPS page through an HTTP proxy:
- Find the proxy. Your device looks up the proxy's host name in DNS, unless you entered an IP address.
- Connect to the proxy. A TCP connection opens between you and the proxy server.
- Open the tunnel. Your client sends a
CONNECTrequest naming the site; the proxy looks up the site, connects to it and replies "200". MDN's description of CONNECT explains that from then on the proxy forwards bytes both ways without reading them. - Secure the connection. Your client and the site run the TLS handshake through the tunnel, so each handshake message travels you, proxy, site and back.
- Wait for the first byte. The site prepares the answer and the first byte comes back. This wait is called TTFB, time to first byte.
- Download the rest. The remaining bytes flow at the speed of the slowest link on the path.
Stages 2 to 4 are set-up: they happen once per connection, not once per request. That fact explains a large share of slow proxy setups.
| Stage | curl field | What makes it slow |
|---|---|---|
| Name lookup | time_namelookup | Slow resolver, uncached name |
| Connect to proxy | time_connect | Slow path to the proxy |
| Tunnel and TLS | time_appconnect | Far exit, new connection each time |
| First byte | time_starttransfer | Slow site, throttling, busy exit line |
| Download | time_total | Bandwidth of the slowest link |
How do you measure where the time goes?
curl can print how long each stage took, so one run with and one without the proxy show where the extra time appears. It comes with Windows 10 and 11, macOS and most Linux systems. Save these lines in a file called timing.txt:
dns lookup:   %{time_namelookup}\n
connect:      %{time_connect}\n
tls:          %{time_appconnect}\n
first byte:   %{time_starttransfer}\n
total:        %{time_total}\n
new conns:    %{num_connects}\n
proxy reply:  %{http_connect}\n
Then run the request directly, and once more through the proxy with -x:
curl -o NUL -s -w "@timing.txt" https://example.com
curl -x http://user:pass@pr.proxynet.io:8000 -o NUL -s -w "@timing.txt" https://example.com
On a Mac or Linux, write -o /dev/null instead of -o NUL; in Windows PowerShell, type curl.exe. Each value is in seconds from the start of the request, as the curl manual's -w section defines it. new conns counts connections the request had to open, and proxy reply is the proxy's answer to CONNECT (000 without a proxy).
On our Windows 11 test machine, a direct request to example.com printed this on 19 November 2026:
dns lookup:   0.014323
connect:      0.026137
tls:          0.045997
first byte:   0.062869
total:        0.062913
new conns:    1
proxy reply:  000
We then sent the same request through a small test proxy running on the same computer, which adds almost no distance:
dns lookup:   0.000041
connect:      0.000504
tls:          0.046269
first byte:   0.062912
total:        0.062954
new conns:    1
proxy reply:  200
The first byte arrived at the same moment, but the stages moved. DNS dropped to almost nothing because the proxy looked up example.com, "connect" now measures the connection to the proxy, and reaching the site moved into "tls". With a real remote proxy, the stage that grows most points to the cause.
How do you read the numbers?
Compare the gaps between stages, not the totals: subtract each line from the next and see which step grew with the proxy on.
- "connect" is large: the path from you to the proxy is slow.
- The gap from "connect" to "tls" is large: reaching the site from the exit takes long, because of distance, routing or DNS.
- The gap from "tls" to "first byte" is large: the site is slow to answer, slows this address down, or the exit's line is busy.
- The gap from "first byte" to "total" is large: bandwidth limits the download.
- "new conns" is 1 on every request: nothing is reused, and every request pays the full set-up.
Run each version 10 to 20 times and compare the median, the middle value, rather than the best or worst run. Proxied timings vary more than direct ones.
What are the most common causes of a slow proxy?
Most slow proxies come down to the eight causes below, in the order you can check them; the first ones are also the cheapest to fix.
The exit is far from the target site
Exit location is the biggest single factor, because every round trip after the tunnel opens travels from you to the exit, from the exit to the site and back. An exit in the site's own country keeps the last leg short; an exit on another continent adds two long legs to each round trip, and a handshake plus a request need several of them. When the job does not need one country's view of the site, choose the exit by where the site is served from.
Every request opens a new connection
A tool that opens a fresh connection per request pays for the tunnel and the TLS handshake each time. For HTTPS sites, a rotating proxy set to a new IP on every request needs a new tunnel for each one, and a script that creates a new HTTP client for each call does the same.
On our test machine we made the test proxy wait 100 ms before opening each new connection to the site, to imitate a distant exit. Five separate requests needed about 160 ms each to the first byte, roughly 0.8 seconds in all. The same five over one reused connection took 161 ms for the first and about 16 ms for each of the others, roughly 0.22 seconds, with new conns: 0 on the reused ones. A real distant exit also slows every later round trip, so the gain is smaller in practice, but the direction holds.
The fix is to reuse connections: keep-alive in your HTTP client, one client object shared across requests, and a sticky session, which keeps the same exit IP for a period you choose (1 to 60 minutes on our residential and mobile proxies).
DNS is resolved in the wrong place
Where the site's name is looked up changes which server you reach. Many large sites answer DNS with a server near whoever asks, so if your computer does the lookup while the exit is abroad, the exit may be sent to a server near you, and every round trip detours. With an HTTP proxy and HTTPS sites, the proxy resolves the name, as our test showed. With SOCKS5 it depends on the client: in curl, socks5:// resolves names on your computer, while socks5h:// hands the name to the proxy. Browsers and libraries usually call this setting remote DNS.
Too many parallel requests on your side
More parallel requests do not always mean more speed. Every connection shares the capacity of your line, and HTTP libraries cap how many connections they open per host, so requests above the cap wait in a queue; browsers, for example, commonly open about six per host over HTTP/1.1. If timings get worse as you raise concurrency and the site returns no errors, the queue is likely on your side. Halve the number of parallel requests and compare the median.
The target site is slowing you down
A site can answer slowly on purpose when one address sends many requests in a short time. The clear signal is HTTP status 429, "Too Many Requests"; MDN's 429 reference notes that such limits are typically tied to the client's IP and that a Retry-After header may say how long to wait. Some sites return no error and only stretch the wait before the first byte.
If the first-byte gap grows on one site while other sites through the same exit stay quick, the site is the bottleneck. The fix is to slow down: honour Retry-After, spread requests over time and stay within the site's terms and robots.txt rules. Spreading the same volume over more addresses to get around a limit is not a fix.
The proxy type does not fit the job
Proxy types differ in where the exit's connection lives, and that shows in timings. Residential and mobile exits sit on real household and mobile connections, so their speed varies with the line and the time of day; datacenter exits sit on server networks with steady capacity. Our comparison of residential and datacenter proxies covers the other differences, such as how sites treat each type.
For work where steady timings matter more than a household address, such as checking an API every few minutes or downloading large files, a Datacenter Proxy keeps its exits in TIER 3+ data centres.
When the job needs one address for weeks and that address should be registered to an internet provider, a ISP Proxy combines a fixed ISP address with data-centre hosting.
Your own connection is the limit
Everything through the proxy also travels over your own line, where weak Wi-Fi, a cloud backup filling the upload or a mobile hotspot add delay. If the direct curl timings are also high or jumpy, fix the local connection first.
Security software inspects encrypted traffic
Some antivirus and company security tools open HTTPS connections to scan them, which adds work to every handshake. View a site's certificate in your browser: if the issuer is your security software rather than a public certificate authority, the traffic is being inspected. Compare timings from another device, and ask your IT team before changing security settings on a work computer.
Does a proxy slow down your internet?
A proxy adds a little delay to every request because traffic makes an extra stop, but with a well-placed exit and reused connections the difference is small for normal browsing. An exit near both you and the site adds a few milliseconds per round trip, while one on another continent can add a hundred milliseconds or more to each. Download speed is capped by the slowest link, so an exit on a server network rarely limits a home connection, while a home-line exit can.
If everything feels slower with the proxy on, send only the traffic that needs it through the proxy; most proxy settings have an exception list for addresses that should go direct.
Where slow proxies cost the most
- Price and stock monitoring: thousands of small requests, where set-up per request adds up to hours.
- API checks from several countries: timings are part of the result.
- Ad and page checks: pages with many resources open many connections.
- Large downloads: throughput, not latency, decides the time.
- Browser test automation: a slow first byte stretches every page load.
Common mistakes
- Measuring once. Compare medians of 10 to 20 runs.
- Testing against another site than the job uses. A speed test server near you says nothing about the route to the target.
- Rotating the IP on every request without need. It throws away connection reuse.
- Choosing the exit by your own location. The site's location matters more for timings.
- Raising concurrency to fix slowness. If the site answers 429 or your queue grows, it makes things worse.
- Very long timeouts. In curl,
--connect-timeoutlimits only the connection phase and--max-timethe whole request; short values surface slow exits quickly.
Decision guide
| Symptom | Likely cause | Fix |
|---|---|---|
| "connect" high | Slow path to the proxy | Check your line, use a cable |
| Gap to "tls" high | Exit far from the site | Exit in the site's country |
| "new conns" 1 every time | No connection reuse | Keep-alive, sticky session |
| Slow on one site only | Site throttling | Slow down, honour Retry-After |
| HTTP 429 responses | Rate limit | Fewer parallel requests |
| Timings jump around | Home or mobile exit line | Datacenter or static ISP proxy |
| Direct also slow | Your own connection | Cable, pause uploads |
Frequently asked questions
Why is my proxy so slow all of a sudden?
Usually something changed: a different exit after a rotation, a site that started rate limiting you, or your own line. Compare a fresh curl timing run with an earlier one; the stage that grew tells you which.
How do I test proxy speed?
Use the curl -w timing template from this article, once directly and once through the proxy, against the site you actually work with. Repeat each 10 to 20 times and compare the medians of "first byte" and "total". Speed test websites measure the route to their own servers, not to your target.
Is SOCKS5 faster than an HTTP proxy?
Usually not by a noticeable amount. With username and password, SOCKS5 exchanges a greeting, a login and a connect request before data flows, while an HTTP proxy needs one CONNECT request, so SOCKS5 adds a couple of short round trips to the proxy. Exit location and connection reuse matter far more.
Are residential proxies slower than datacenter proxies?
Often, and they vary more. A residential exit runs on a household connection whose speed depends on the line and its load, while a datacenter exit runs on server networks with steady capacity. For small web requests the difference can be minor; for large downloads it shows.
What is a proxy timeout error?
A proxy timeout means a step took longer than the limit set in your client or on the proxy, so the request was cancelled. Common reasons are an exit that cannot reach the site, a site that holds the request open, or a limit too low for a distant exit; find the stalled stage before raising the limit.
Do rotating proxies make requests slower?
Rotating on every request makes each one pay the full set-up: a new connection to the proxy, a new tunnel and a new TLS handshake. Rotation on a timer, or a sticky session for related requests, keeps the connection open and saves that time.
Summary
A slow proxy is a measurement problem before it is a settings problem. Split one request into stages with curl -w, compare it with a direct run and see which gap grew: set-up points to exit distance or missing connection reuse, the first-byte wait to the site or the exit's line, a long download to bandwidth. Then fix the cause with an exit near the site, reused connections, DNS on the proxy side, fewer parallel requests and a proxy type that fits the job. To compare exit locations and proxy types, see our proxy products.